Fullview รวบรวม log นับสิบล้านรายการต่อวันจากทุกไซต์ กลั่นเป็นหลักฐานที่เข้าใจง่ายด้วย AI ซึ่งประมวลผลภายในองค์กร ข้อมูลไม่ออกสู่คลาวด์ แล้วปิดเหตุการณ์ด้วย Response Ticket ที่มีผู้อนุมัติ มีกรอบเวลา และตรวจสอบย้อนหลังได้ทุกขั้นตอน Fullview collects tens of millions of log lines a day from every site and distills them into clear evidence with AI that runs inside your organization. Nothing ever leaves for the cloud. It then closes each incident with a Response Ticket that has an approver, a time window, and a complete audit trail.
log สดไหลเข้า Log DNA เพื่อย่อเป็นรหัสรูปแบบ Detector เปรียบเทียบกับเส้นฐานเพื่อตรวจจับความผิดปกติ Alert router ส่งเหตุการณ์ให้ AI Agent สืบค้นหลักฐานผ่าน METALog MCP แล้วสรุปถึงผู้ดูแลพร้อมดำเนินการตาม runbook ดูการทำงานจริงทีละขั้นด้านล่าง Live logs flow into Log DNA and collapse into pattern codes. The Detector compares counters against baselines to catch anomalies. The Alert router hands events to the AI Agent, which gathers evidence through METALog MCP, then reports to the operator and acts along the runbook. Watch it run step by step below (diagram in Thai).
การมองเห็นป้อนหลักฐานให้ AI, AI ป้อนคำแนะนำให้การตอบสนอง และผลการตอบสนองย้อนกลับมาเป็นความรู้ใหม่ของระบบ Visibility feeds evidence to the AI, the AI guides the response, and every response returns as new knowledge for the system.
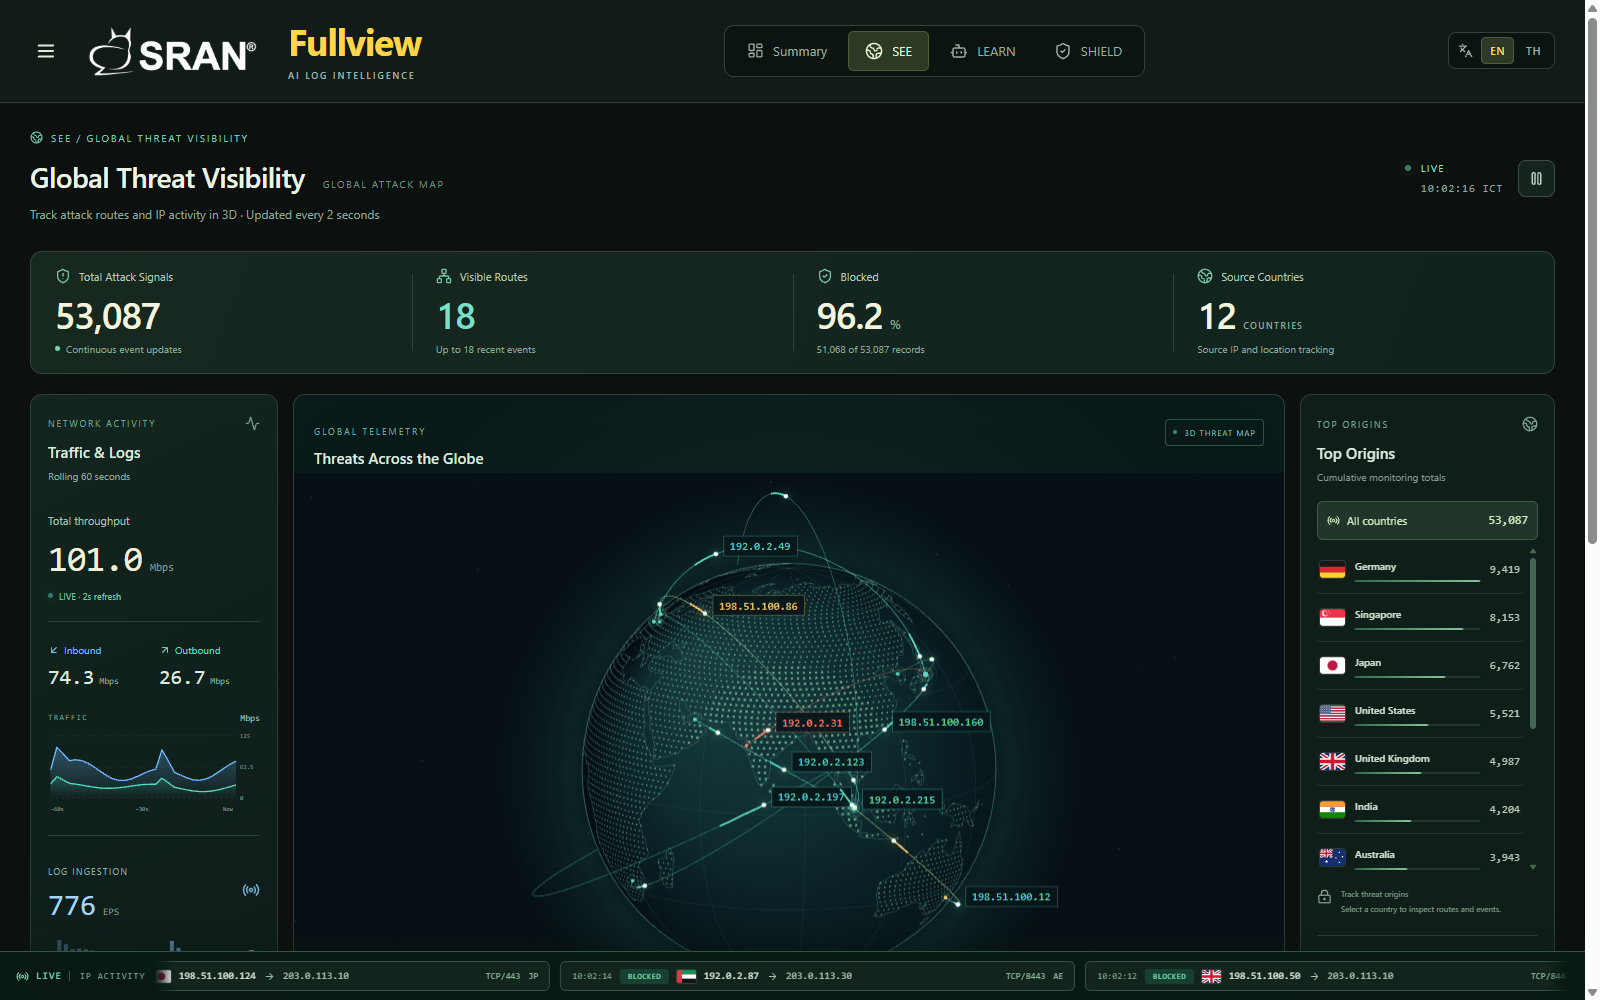
โลก 3D แสดงเส้นทางโจมตีแบบเคลื่อนไหว ทั้งต้นทาง ปลายทาง ประเทศ และสถานะของทุกเหตุการณ์ พร้อมรายการเหตุการณ์ที่กำลังเกิดขึ้นให้เจาะดูรายละเอียดได้ทันที A 3D globe animates every attack route, source, destination, country, and the status of each event, beside a live feed you can drill into instantly.
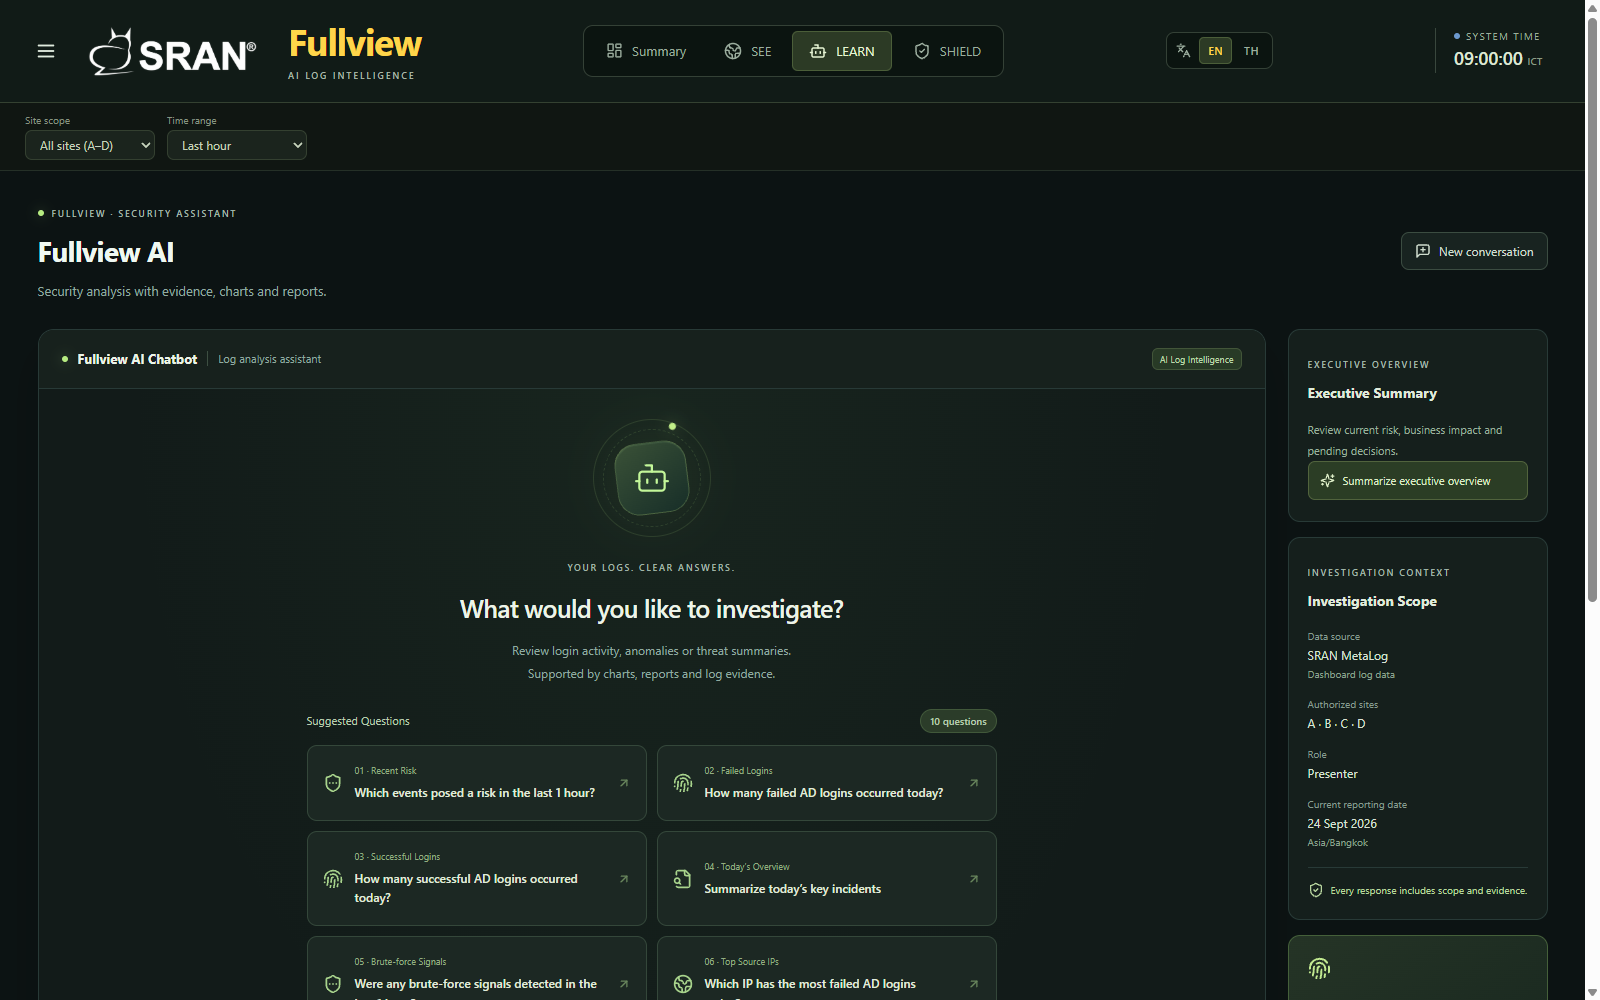
Security Chatbot ประมวลผลบน LLM ภายในองค์กร สอบถามข้อมูล log เหตุการณ์ หรืออุปกรณ์ใด ๆ ด้วยภาษาทั่วไป หรือส่งเหตุการณ์เข้า AI Investigation เพื่อให้ AI สืบค้นหลักฐานผ่าน METALog MCP โดยข้อมูลไม่ออกจากเครือข่ายแม้แต่ไบต์เดียว The Security Chatbot runs on an in-house LLM, ask about any log, event, or host in everyday language, or send an event to AI Investigation and let the AI gather evidence through METALog MCP. Not a single byte of your data leaves the network.
ภัยคุกคามที่ยืนยันแล้วจะกลายเป็น Response Ticket: เปิด → อนุมัติ → ส่งต่อ → ยืนยันผล โดย Firewall, EDR และ WAF เป็นผู้บังคับใช้มาตรการ ส่วน SHIELD ติดตามทุกคำขอ กรอบเวลา และการคืนค่า ไม่มีการดำเนินการใดที่ปราศจากบันทึก A confirmed threat becomes a Response Ticket: open → approve → dispatch → verify. Firewall, EDR, and WAF enforce the measure while SHIELD tracks every request, its time window, and its rollback, nothing happens without a record.
เก้าโมดูลบนคอนโซลเดียว ตั้งแต่ภาพรวมสำหรับผู้บริหารจนถึงหลักฐานรายการ log Nine modules on a single console, from the executive overview down to per-log evidence.
สรุปสถานะทั้งองค์กรบนหน้าเดียว ทั้งปริมาณ log ภัยคุกคามที่พบ คะแนนความเสี่ยง และเหตุการณ์ล่าสุดThe whole organization on one page, log volume, detected threats, risk score, and the latest events.
โลก 3D แสดงเส้นทางโจมตีและ IP แบบเคลื่อนไหว พร้อมรายการเหตุการณ์เรียลไทม์และตัวกรองประเทศA 3D globe of animated attack routes and IPs, with a live event list and per-country filters.
สอบถามและตอบด้วยภาษาทั่วไปบน LLM ภายในองค์กร แล้วส่งประเด็นที่สงสัยไปวิเคราะห์ต่อได้ทันทีPlain-language Q&A on an in-house LLM, escalate anything suspicious for deeper analysis in one click.
เปิด อนุมัติ ส่งต่อ และยืนยันผลมาตรการป้องกัน โดยมีกรอบเวลาและการคืนค่าอัตโนมัติOpen, approve, dispatch, and verify containment measures, time-boxed with automatic restore.
ติดตามเส้นทางของ log ทีละขั้น ตั้งแต่ Log DNA, Detector, Alert router จนถึงคำตัดสินของ AITrace each log's journey step by step, Log DNA, Detector, Alert router, through to the AI's verdict.
ค้นหาและกรอง log หลายล้านบรรทัดตามช่วงเวลา แหล่งที่มา และรูปแบบ ได้ในไม่กี่วินาทีSearch and filter millions of log lines by time range, source, and pattern, in seconds.
ส่งเหตุการณ์ให้ AI Agent สืบค้นหลักฐานผ่าน METALog MCP: search_logs · get_counts · ack_alertHand an event to the AI Agent to gather evidence through METALog MCP, search_logs · get_counts · ack_alert.
ทุก incident ผูกหลักฐานอ้างอิงครบถ้วน พร้อมส่งออกรายงานประกอบการตรวจสอบและ complianceEvery incident is bound to its supporting evidence, exportable for audits and compliance.
แสดงสถานะเซนเซอร์และไซต์ทั้งหมดในที่เดียว รองรับหลายไซต์ (multi-site) จากคอนโซลกลางSensor and site health in one place, multi-site, managed from a central console.
log คือข้อมูลที่อ่อนไหวที่สุดชิ้นหนึ่งขององค์กร Fullview จึงออกแบบให้ AI เข้ามาหาข้อมูล ไม่ใช่ส่งข้อมูลออกไปหา AI Logs are among the most sensitive data an organization holds, so Fullview brings the AI to the data, never the data to the AI.
AI Agent ประมวลผลบนฮาร์ดแวร์ขององค์กร (เช่น AI Workstation ระดับ RTX PRO 6000) วิเคราะห์ได้แม้ในเครือข่ายปิด (air-gapped)The AI Agent runs on your own hardware (e.g., an RTX PRO 6000-class AI workstation), even in air-gapped networks.
ไม่ส่งข้อมูลไปคลาวด์ ไม่มี third-party API สอดคล้องกับ PDPA และข้อกำหนดข้อมูลของหน่วยงานภาครัฐ/CIINo cloud upload, no third-party APIs, aligned with PDPA and government / CII data requirements.
AI สืบค้นหลักฐานผ่าน METALog MCP server ด้วยสิทธิ์ที่จำกัดและตรวจสอบได้ ทุกการเรียกใช้ถือเป็น audit eventThe AI gathers evidence through the METALog MCP server with limited, auditable permissions, every call is an audit event.
รับ log และ mirror traffic โดยไม่แตะเส้นทางข้อมูลจริง ระบบเดิมทำงานต่อเนื่อง ไม่มี single point of failureIngests logs and mirrored traffic without touching the live data path, no downtime, no single point of failure.
องค์ประกอบของ Local AI สำหรับวิเคราะห์ log คือโครงสร้างภายในระบบ AI ขององค์กร สำหรับดึง log จาก MetaLog วิเคราะห์ เชื่อมโยงเหตุการณ์ และสรุปผล โดยทุกส่วนประมวลผลแบบ On-Premises The components of Local AI for log analysis, the internal structure that pulls logs from MetaLog, analyzes them, correlates events, and produces conclusions. Every part runs on-premises (diagram in Thai).
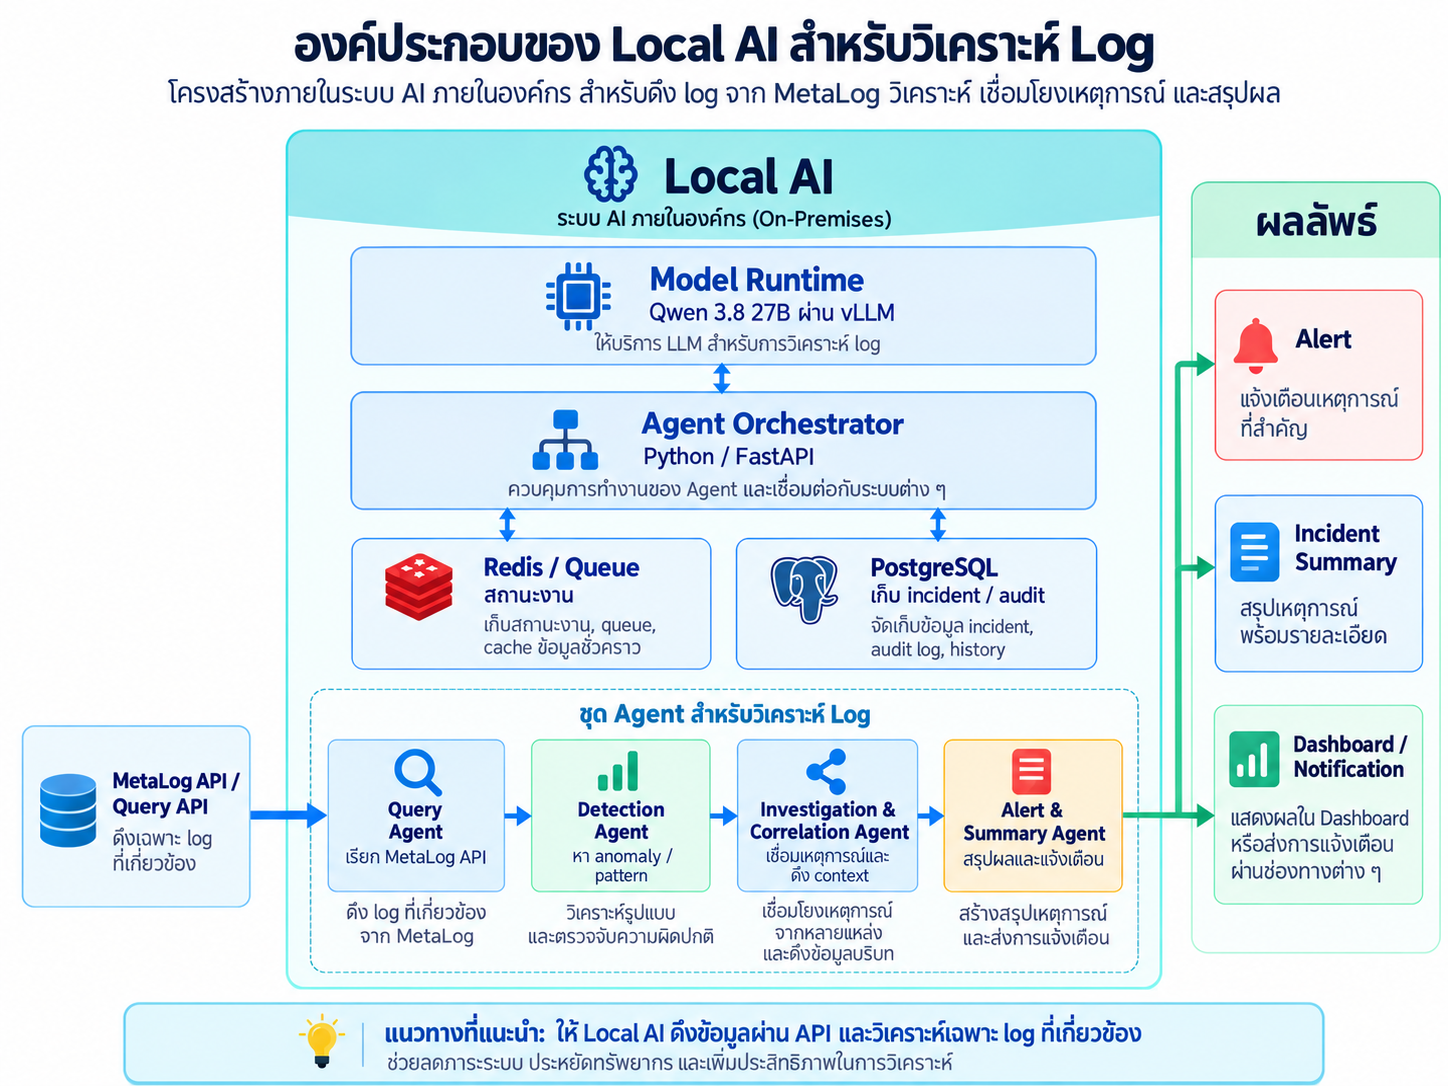
จุดเริ่มต้นของทุกการวิเคราะห์ เมื่อมีเหตุการณ์หรือคำสั่งสืบค้น Query Agent จะเรียก MetaLog API / Query API เพื่อดึงเฉพาะ log ที่เกี่ยวข้องกับเรื่องนั้น ไม่ดึงข้อมูลทั้งระบบ จึงลดภาระระบบและได้ผลลัพธ์รวดเร็ว Where every analysis starts, on an event or a query, the Query Agent calls the MetaLog API / Query API to pull only the logs relevant to that case. No full-system sweeps, so the load stays low and answers come fast.
รับ log จาก Query Agent มาวิเคราะห์รูปแบบ เปรียบเทียบพฤติกรรมกับเส้นฐาน ตรวจจับความผิดปกติ ความถี่ที่เพิ่มสูงผิดปกติ และรูปแบบใหม่ที่ไม่เคยพบมาก่อน แล้วส่งประเด็นที่น่าสงสัยต่อให้ขั้นถัดไป Takes the pulled logs and analyzes their patterns, comparing behavior against baselines, catching anomalies, suspicious frequency spikes, and never-seen patterns, then passes anything suspicious downstream.
สืบสวนเชิงลึก เชื่อมโยงเหตุการณ์จากหลายแหล่งเข้าด้วยกัน (เครื่อง บัญชีผู้ใช้ ช่วงเวลา) และดึงข้อมูลบริบทเพิ่มเติมจนเข้าใจเหตุการณ์ที่เกิดขึ้นอย่างครบถ้วน ไม่ใช่เพียงการแจ้งเตือนที่แยกส่วน The deep-dive step, linking events from multiple sources (hosts, accounts, time windows) and pulling extra context until the real story emerges, not just an isolated alert.
ขั้นตอนสุดท้ายของกระบวนการ จัดทำสรุปเหตุการณ์ที่เข้าใจง่าย พร้อมหลักฐานประกอบ แล้วส่งออกเป็น Alert สำหรับเหตุการณ์สำคัญ, Incident Summary และแสดงผลบน Dashboard หรือแจ้งเตือนผ่านช่องทางต่าง ๆ The end of the pipeline, producing readable incident summaries with their evidence, emitted as critical Alerts, Incident Summaries, and Dashboard views or notifications across your channels.
Qwen 3.8 27B ผ่าน vLLM ให้บริการ LLM สำหรับการวิเคราะห์ log ภายในองค์กร ไม่ต้องพึ่งพาบริการภายนอกQwen 3.8 27B served via vLLM, the LLM behind all log analysis, running locally with no external service.
Python / FastAPI ควบคุมลำดับการทำงานของ Agent ทั้งชุด และเชื่อมต่อกับระบบต่าง ๆ รอบข้างPython / FastAPI, sequences the whole agent chain and connects it to surrounding systems.
จัดเก็บสถานะงาน คิวงาน และ cache ข้อมูลชั่วคราว ให้ Agent หลายตัวทำงานพร้อมกันได้โดยไม่รบกวนกันHolds job state, queues, and short-lived caches, letting multiple agents work in parallel without collisions.
จัดเก็บ incident, audit log และประวัติการวิเคราะห์ทั้งหมด ตรวจสอบย้อนหลังได้ทุกการตัดสินใจของ AIStores incidents, audit logs, and full analysis history, every AI decision can be reviewed later.
แนวทางที่แนะนำ:Recommended approach: ให้ Local AI ดึงข้อมูลผ่าน API และวิเคราะห์เฉพาะ log ที่เกี่ยวข้อง ซึ่งช่วยลดภาระระบบ ประหยัดทรัพยากร และเพิ่มประสิทธิภาพในการวิเคราะห์ let Local AI fetch data through APIs and analyze only the relevant logs, reducing system load, saving resources, and making every analysis more efficient.
 Fullview